
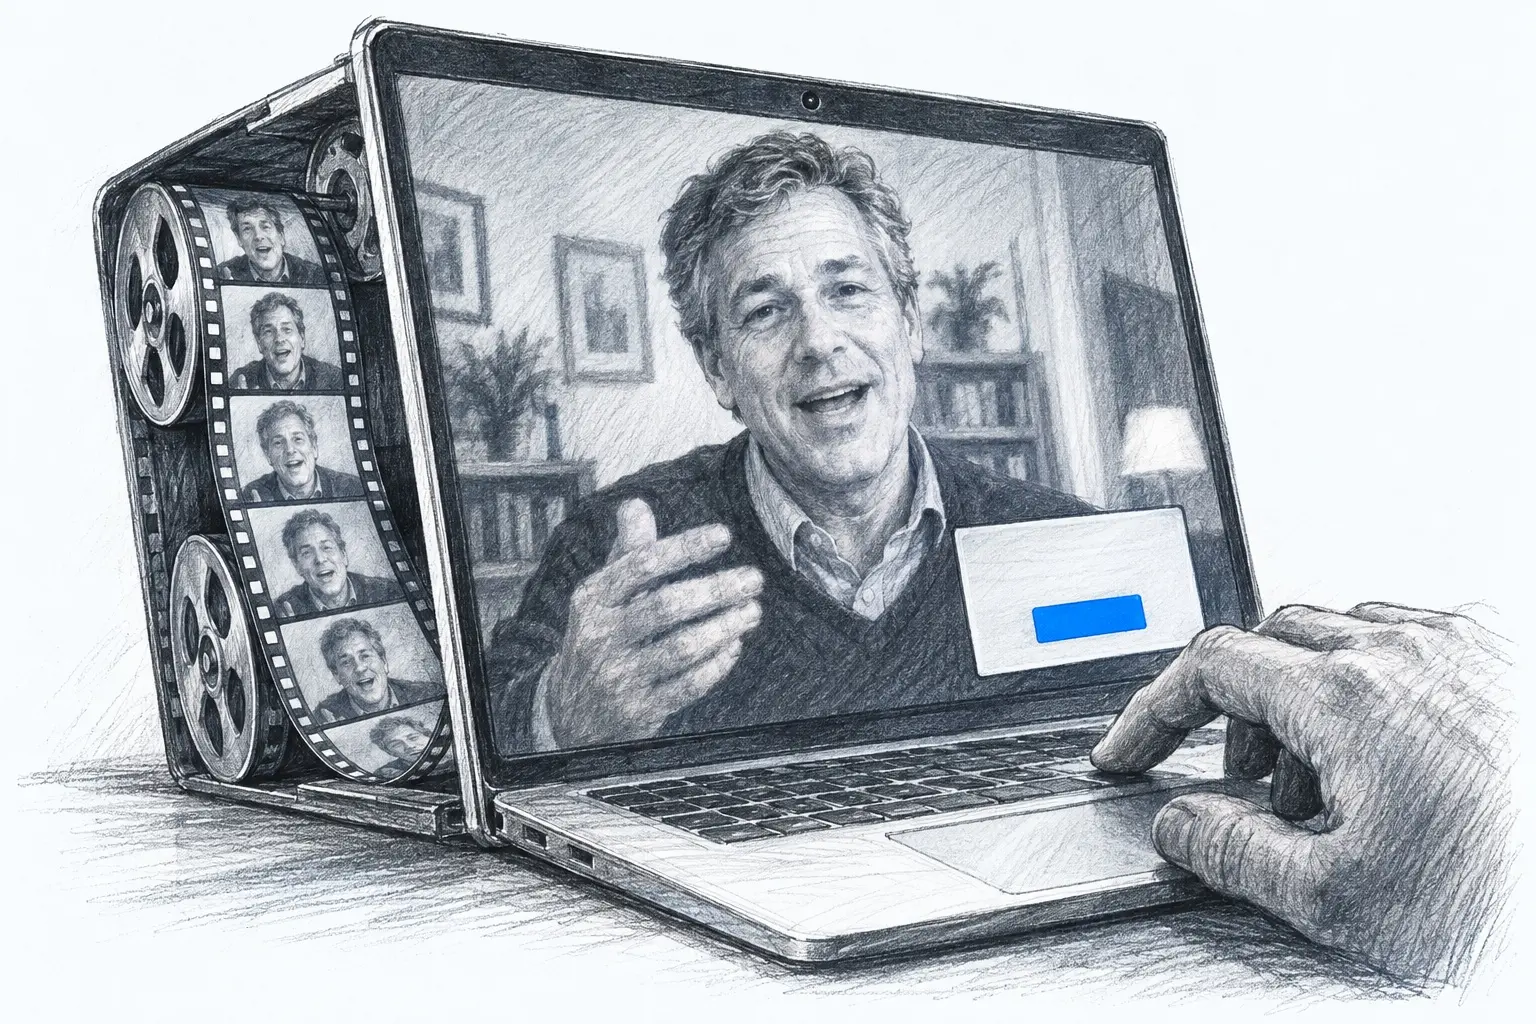
The Most Convincing Person on That Video Call Was Real. They Just Weren't There.
The FBI just disrupted a North Korean operation that stole more than $400 million in cryptocurrency over 18 months. They called it FaceStealer. When agents seized the servers, they found over 900 webcam videos of victims — people who thought they were on a normal video call with someone they knew.
Here's what makes this different from every deepfake panic you've read about: the person on screen was completely real. No synthetic voice. No AI-generated face. Just your colleague, mouthing words on a silent call, while malware moved through your network and your webcam quietly recorded the next victim.
I've spent twenty years watching social engineering evolve, and this scheme represents something more sophisticated than the technology itself. The attackers didn't need to fake anything. They just needed to understand what we trust.
The Attack Pattern Nobody's Talking About
The setup is elegant in its simplicity. An invite lands in your inbox from someone you've worked with for years. Their account was compromised months ago — you just didn't know it yet. You join what looks like a standard Zoom or Teams meeting.
The familiar face appears on screen. No audio comes through. A chat message explains they can't hear you either, and you need a quick software update to fix the connection. You click the link. The malware installs.
Your webcam was recording from the moment you joined. Your contact list, your face, your mannerisms — all of it gets harvested. Next month, you're the familiar face on someone else's screen, perpetuating the cycle without ever knowing you became part of the attack chain.
The social proof in that meeting was real. It was just borrowed from the previous victim.
Why Your Instinct Is the Vulnerability
I know what I do when audio dies on a call. I start clicking things. I try the settings. I toggle the microphone. I look for a fix because I'm wired to solve the immediate problem in front of me.
Turns out the North Korean cyber units know that about me too. They're counting on it.
The sophistication here isn't technical — it's behavioral. The attackers watched how we actually work and built the exploit around our patterns. We've trained ourselves to expect technical glitches. We've normalized clicking through prompts to stay productive. The friction we removed from remote work became the attack surface.
A familiar face on a screen no longer proves identity. It proves someone had the footage.
I've Watched This Movie Before
Ten years ago, I was advising a financial services client through a business email compromise incident. Their finance team wired $280,000 to an account in Hong Kong because the request came from their CFO's actual email address. The tone was right. The signature matched. The request seemed urgent but not unusual.
The email was real. The CFO just didn't send it.
We built better spam filters after that wave of attacks. We deployed email authentication protocols. We added security training. None of it addressed the core vulnerability: when something looks legitimate, we process it as legitimate, especially under time pressure.
What fixed business email compromise wasn't better technology. It was a simple operational control: if you receive a wire transfer request via email, you hang up and call the number you already have on file. You confirm through a separate channel before you act.
That discipline worked because it interrupted the attack chain at the trust layer, not the technical layer.
We need the same discipline now. Same threat model, different room.
The Three Rules I'm Putting in Front of Teams This Week
I'm not interested in teaching people to spot deepfakes or analyze video artifacts. That's not where this fight happens. The fight happens in the five seconds between seeing something familiar and clicking.
Rule one: Unexpected invite? Confirm it through a channel you already trust. Not a reply to the email. Not a response in chat. Pick up the phone and call the number you've used before, or walk to their office, or send a text to the mobile you have saved. If it's legitimate, you've lost thirty seconds. If it's not, you've stopped the breach.
Rule two: Join from the official app, never a link. If someone sends you a Zoom link, open Zoom yourself and enter the meeting ID manually. If it's Teams, launch Teams and join from there. The extra click removes the opportunity for a spoofed landing page or a malicious installer disguised as the real platform.
Rule three: Nobody, however familiar, hands you a "fix" mid-call. If your audio fails and someone suggests downloading something to resolve it, the call ends. You exit. You contact IT through your normal support channel. You don't troubleshoot with software from an unverified source, even if the person recommending it looks exactly like your coworker.
These aren't technical controls. They're operational ones. They work because they add friction back into the trust handshake — the friction we spent a decade removing because it felt like inefficiency.
The Uncomfortable Question Your Monday Morning Needs
Here's what I want you to sit with: if a partner's audio died on Zoom tomorrow morning, would your people hang up and call back, or would they click through whatever "fix" appeared on screen?
Be honest. Because the answer isn't about their training or their awareness. It's about what we've normalized.
We've built cultures that reward speed and punish friction. We've made "just jump on a quick call" the default for everything. We've removed the callback, the confirmation, the moment of verification, because those things felt like obstacles to productivity.
The North Korean cyber units didn't invent a new exploit. They just watched what we optimized for and built the trap accordingly.
What Monday Morning Looks Like
I'm not asking you to slow down every interaction or treat every colleague like a potential threat. That's not sustainable, and it's not the point.
What I am asking: identify the three interactions in your firm where a compromised trust relationship creates material harm. Wire transfers. Client data access. System administration. Vendor payments. Whatever your version of "$400 million in eighteen months" looks like.
Then build the callback into those workflows. Make the confirmation through a separate channel non-negotiable, not because you don't trust your people, but because you understand the attack assumes you will.
Talk to your team this week. Not about deepfakes or AI or the technical sophistication of nation-state actors. Talk about the moment when something feels slightly off — the audio that won't connect, the unexpected link, the familiar face asking for something unusual.
That's the moment. The discipline you build there is what stands between a normal Tuesday and a very different conversation with your board.
The attackers are patient. They'll wait months between the account compromise and the exploitation. They'll use real footage and real relationships. They'll count on our instinct to solve the immediate problem without pausing to verify the ask.
The question isn't whether the technology will get better. It's whether we'll add back the friction that makes the technology irrelevant.
So: what's your callback? And who on your team knows to use it?
Frequently asked questions
- What is the FaceStealer scheme and how does it work?
- FaceStealer is a North Korean cyber operation that hijacks accounts and lures victims into fake video calls using real footage captured from previous victims' webcams. The attacker impersonates someone the victim knows, claims to have audio issues, and tricks them into downloading malware that steals their contact list—making them the next victim.
- How much money was stolen in the FaceStealer operation?
- Over $400 million in cryptocurrency was stolen across 18 months, with the FBI and Justice Department seizing over 900 webcam videos of victims.
- What three security rules should teams follow to prevent this attack?
- First, confirm unexpected invites through a channel you already trust. Second, join calls only from the official app, never from a link. Third, never accept a 'software fix' during an active call—hang up and call the person back using a number you already have on file.
- Why is this scam more effective than deepfakes?
- It doesn't require perfect deepfakes. Real video footage of a real person combined with a genuinely hijacked account creates authentic social proof—the victim recognizes both the face and the legitimate account, making them far more likely to trust the request.
More Leadership Posts
The Future of Consulting: Embracing AI Without Losing the Human Touch
A deep dive into how management consulting is evolving with AI, featuring insights on client expectations, service deliv...
2 Ways to Learn to Manage
Discover two transformative approaches to mastering management: emulate respected leaders or learn from ineffective mana...
58% of Companies Block Access to Social Media Sites
I recently posted about the benefits of not blocking access to social media websites on the corporate network. Then I pi...